
Cryptographic Attestation Layers
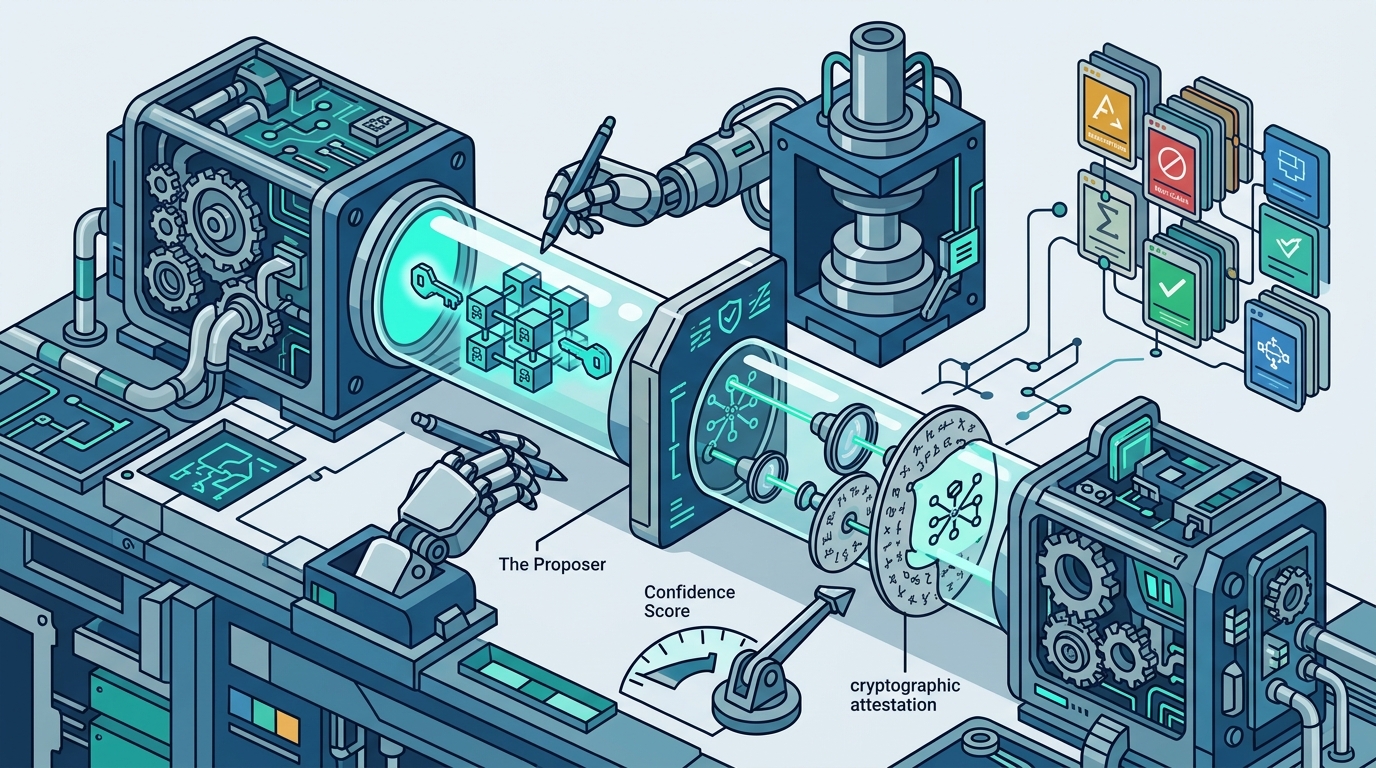
Cryptographic attestation is the process of verifying the integrity and origin of a digital artifact using mathematical proofs. In the context of autonomous infrastructure, this layer ensures that a proposed action has not been tampered with during transit. Verifiable Proof Systems relies on this mechanism to separate the proposer from the executor. The system does not trust the model's confidence score. Instead, it demands a signed artifact that can be independently verified.
Independent Evidence Requirements
Admission into the execution plane requires independent evidence. This evidence must not be produced by the proposing system itself. A model cannot sign its own permission slip. The attestation layer checks for a verified workload identity and a separate human sponsor. This dual-control mechanism prevents a single compromised agent from executing consequential actions. The evidence is bounded and single-use, scoped strictly to the predicted effect of the action.
State and Sequence Continuity
Continuity is a critical component of the attestation layer. The system verifies that the state of the environment has not drifted since the proposal was made. It checks the sequence of previous actions to ensure no unauthorized changes occurred. If the state has changed, the admission check fails. This prevents race conditions where a stale proposal is executed against a new reality. The record of this check is durable and immutable.
The Three-Plane Architecture
The VPS architecture separates computation, authority, and consequence into three distinct planes. This separation is the core of the verifiable authority model. Each plane has a specific role and a strict boundary with the others. The architecture ensures that intelligence can propose, but only verified authority can execute.
Plane A: Proposal
Plane A is the untrusted zone. Models, planners, tools, and humans propose actions here. This plane holds no authority over production state or physical actuators. A proposal is just a candidate action. It is cheap to produce but carries no permission. The system treats every proposal in this plane as unverified testimony. It does not admit the transition to execution based on this plane alone.
Plane B: Admission
Plane B is the deterministic check. It performs a small, fixed-policy check of the attempt and its predicted effect. This is the boundary where a proposed action either becomes a consequence or is refused. The check requires all five assurance conditions to hold together. These include independent evidence, bounded authority, verified identity, state continuity, and declared constraints. If any condition fails, the action is refused and the refusal is recorded.
Plane C: Execution
Plane C is minimal and carries out only what Plane B authorized. It executes the change to authoritative state or to a physical actuator. It records the outcome of the execution. Logging an intent is not a consequence. Only the actual change in state is considered a consequence. This plane is designed to be as small and auditable as possible.
Mutual NDA as Collaboration Foundation
A mutual NDA is a legal agreement where both parties agree to protect shared confidential information. In the VPS model, this legal framework serves as the trust foundation for B2B collaboration. It allows design partners to share system boundaries and internal designs without fear of intellectual property theft. This trust is essential for the pilot phase. It enables the exchange of the specific data needed to define the admission boundary.
Defining System Boundaries
Under the mutual NDA, partners work with VPS to define the boundaries of their systems. VPS uses custom tools written in DARKc, a formally verified fail-closed compiler syntax. These tools surface points where boundaries are weak, drifted, or non-existent. The AgenticX-DYE(TM) tool is used to visualize these weak points. This process helps partners understand where their current systems lack verifiable authority. It identifies the gaps that the VPS infrastructure can address.
Confidentiality and Trust
The mutual NDA ensures that the detailed system maps and boundary definitions remain confidential. This is critical for companies operating in sensitive sectors. It allows for a deep technical assessment without exposing proprietary logic to competitors. The legal protection provided by the NDA complements the technical protection provided by the cryptographic attestation layers. Together, they create a robust environment for collaboration.
The Admission Boundary
The admission boundary is the single point where a proposed action is checked against the policy. It is the gatekeeper of the system. Every decision at this boundary is recorded, including refusals. This creates a complete audit trail of all attempted actions. The boundary is deterministic, meaning the same input will always produce the same output under the same policy. This predictability is essential for formal verification.
The Five Assurance Conditions
Admission requires five conditions to be satisfied simultaneously. First, independent evidence must be present. Second, bounded, single-use authority must be scoped to the predicted effect. Third, a verified workload identity and a separate human sponsor must be confirmed. Fourth, state and sequence continuity must be verified. Fifth, declared constraints must be satisfied. If any one of these fails, the action is refused. This all-or-nothing approach prevents partial authorization.
Durable Decision Records
Before any effect occurs, a durable decision record is created. This record captures the state of the system, the evidence provided, and the decision made. It is tamper-evident, meaning any attempt to alter it can be detected. The record includes the refusal of actions that did not meet the criteria. This comprehensive logging allows for post-hoc analysis and debugging. It provides the data needed to refine the policy over time.
Design Partner Pilot Structure
The design partner pilot is a four-week, fixed-fee engagement. It focuses on one of the partner's systems. The goal is to apply the VPS framework to a real-world scenario. The pilot closes with a letter of intent if the criteria agreed in week one are met. This structure provides a low-risk way for companies to evaluate the infrastructure. It allows for a practical reality check before a full commitment.
Week One: Criteria Agreement
In the first week, VPS and the design partner agree on the success criteria. These criteria are specific and measurable. They define what a successful integration looks like. This step ensures that both parties have aligned expectations. It prevents scope creep and keeps the pilot focused. The criteria are documented in the mutual NDA framework.
Weeks Two to Three: Implementation and Testing
During the middle weeks, the VPS tools are applied to the partner's system. The AgenticX-DYE(TM) tool is used to map the boundaries. The admission boundary is configured with the partner's specific policy. The system is tested with various proposed actions, including those that should be refused. The results are analyzed to identify any gaps in the current setup.
Week Four: Evaluation and LOI
In the final week, the results are evaluated against the week one criteria. If the criteria are met, a letter of intent is issued. This LOI outlines the next steps for a full deployment. If the criteria are not met, the pilot ends, and the findings are shared. This transparent process builds trust and demonstrates the value of the VPS approach.
Key Takeaways
- The three-plane architecture separates proposal, admission, and execution to prevent unauthorized actions.
- Admission requires five assurance conditions, including independent evidence and bounded authority.
- Cryptographic attestation ensures the integrity of proposed actions and system state.
- The AgenticX-DYE(TM) tool helps identify weak or drifted system boundaries.
- The design partner pilot is a four-week, fixed-fee engagement that ends with a letter of intent.
- Every decision at the admission boundary is recorded, including refusals, creating a durable audit trail.
- VPS is a research initiative, and CEAK-PRO 1.0 is a conceptual working paper, not a certified product.
Frequently Asked Questions
What is the core function of the admission boundary?
The admission boundary is a deterministic check that verifies if a proposed action meets all five assurance conditions. It decides whether the action becomes a consequence or is refused.
How does the mutual NDA protect the design partner?
The mutual NDA ensures that confidential information shared during the pilot, such as system boundaries and internal designs, is protected from disclosure to third parties.
What is the difference between Plane A and Plane B?
Plane A is the untrusted proposal zone where actions are generated. Plane B is the admission zone where actions are checked against a fixed policy before execution.
Is the VPS system formally verified?
CEAK-PRO 1.0 is a conceptual working paper. It reports no model-checking, proof, or implementation results. Formal models and an implementation are in development for a companion paper.
What tools does VPS use to define system boundaries?
VPS uses custom tools written in DARKc, a formally verified fail-closed compiler syntax. The AgenticX-DYE(TM) tool is used to surface points where boundaries are weak or non-existent.
How long does the design partner pilot last?
The design partner pilot is a four-week, fixed-fee engagement on one of the partner's systems. It closes with a letter of intent if the agreed criteria are met.