
Verifiable Authority Design Methodologies: A 2026 Implementation Guide
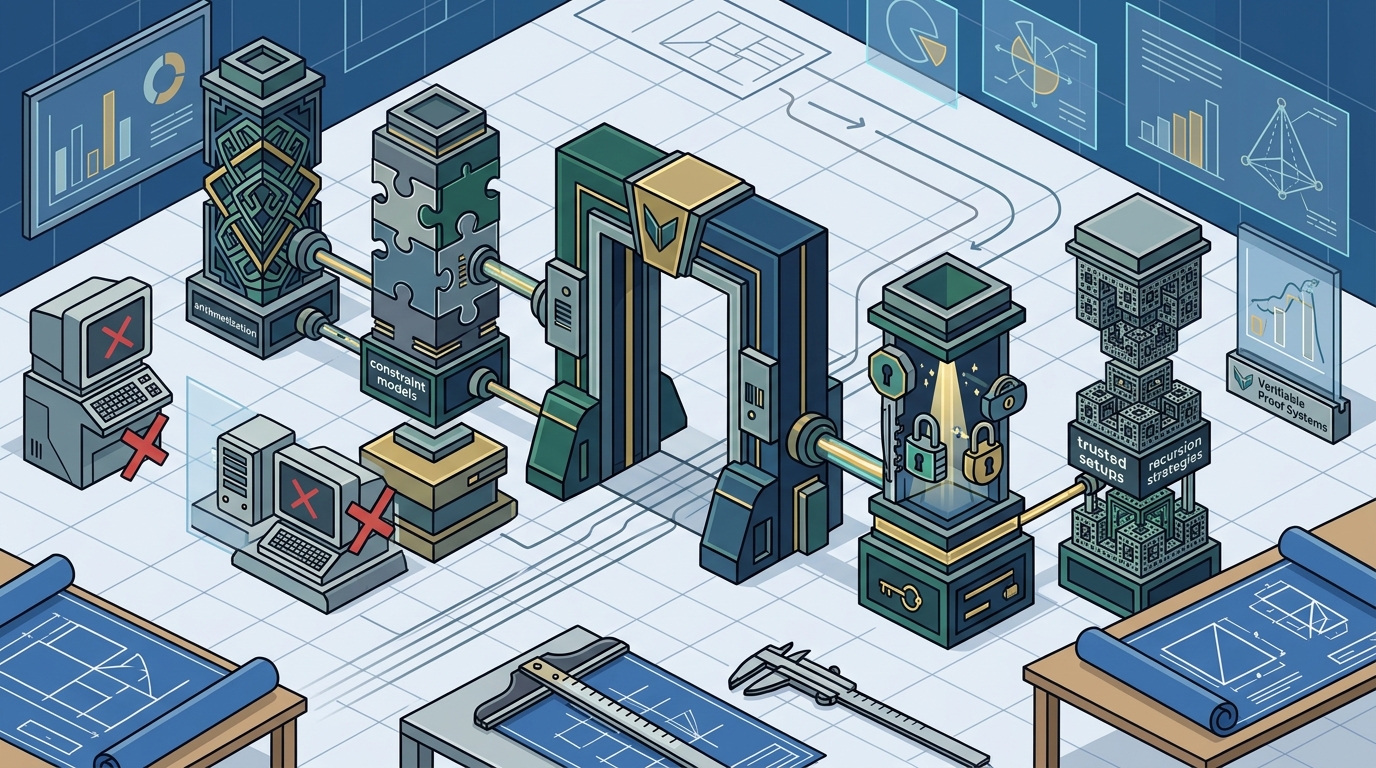
Verifiable Proof Systems (VPS) separates computation, authority, and consequence at a single admission boundary. This approach differs from standard proof systems by requiring five independent assurance conditions to hold simultaneously before any state change occurs. This guide covers how VPS design methodologies differ from other leading proof systems in terms of implementation, focusing on arithmetization, constraint models, commitment schemes, trusted setups, and recursion strategies.
Proof System Arithmetization
Arithmetization is the process of translating computational logic into algebraic constraints that can be verified mathematically. In traditional zero-knowledge proof systems, this often involves converting Boolean circuits into polynomial equations. Verifiable Proof Systems approaches this differently by focusing on the boundary between proposal and execution rather than the internal logic of the computation itself. The goal is not to prove that a computation was performed correctly in a vacuum, but to prove that a specific action is authorized under a fixed policy.
From Circuit to Boundary
Standard systems often rely on heavy arithmetization of the entire program flow. VPS instead arithmetizes the admission check. This check is small and deterministic. It verifies the attempt and its predicted effect under a fixed policy. This distinction is critical for implementation because it reduces the complexity of the proof generation phase. The proof does not need to cover the entire history of the agent, only the specific transition from proposal to consequence.
Implementation Implications
By isolating the admission boundary, VPS allows for more efficient verification. The verifier does not need to trust the proposer's internal state. It only needs to verify that the five assurance conditions are met. This includes independent evidence, bounded authority, verified identity, state continuity, and declared constraints. This modular approach makes it easier to integrate with existing infrastructure without requiring a complete overhaul of the underlying computational engine.
Constraint Models
A constraint model is a formal specification of the rules that govern what actions are permitted. In many proof systems, constraints are static and defined at deployment time. Verifiable Proof Systems uses dynamic constraint models that are scoped to the predicted effect of a specific action. This means the constraints are not just about what the system can do, but what it is allowed to do in a specific context.
Dynamic Scoping
Traditional models often use broad permission sets. VPS uses bounded, single-use authority. This authority is scoped to the predicted effect. If the predicted effect changes, the authority must be re-evaluated. This prevents privilege escalation and ensures that the system operates within strict limits. The constraint model is therefore not a static list of permissions, but a dynamic check that adapts to the specific proposal.
Policy Enforcement
The constraint model is enforced at the admission boundary. This is where the system decides whether to admit or refuse the action. The decision is recorded, including refusals. This creates an audit trail that is essential for accountability. The constraint model is not just a technical component, but a governance mechanism. It ensures that the system's behavior is aligned with the organization's policies and regulatory requirements.
Commitment Schemes
A commitment scheme is a cryptographic primitive that allows a party to commit to a value without revealing it. In proof systems, commitment schemes are used to ensure that the prover cannot change the inputs after the proof is generated. Verifiable Proof Systems uses commitment schemes to bind the proposer's identity and the predicted effect of the action. This ensures that the proof is valid for the specific action that was proposed.
Binding Identity and Effect
The commitment scheme binds the verified workload identity to the predicted effect. This prevents the proposer from claiming a different identity or a different effect after the fact. The commitment is opened only when the action is executed. This ensures that the proof is valid for the specific action that was taken. The commitment scheme is a critical component of the admission boundary, as it ensures that the proposer cannot repudiate their actions.
Efficiency and Security
Trusted Setup Requirements
A trusted setup is a process that generates cryptographic parameters that are used in the proof system. In many zero-knowledge proof systems, the trusted setup is a single point of failure. If the setup is compromised, the entire system is compromised. Verifiable Proof Systems aims to minimize the need for a trusted setup by using transparent and verifiable parameters. This reduces the risk of compromise and increases the trust in the system.
Transparent Parameters
VPS uses transparent parameters that can be verified by anyone. This means that the parameters are not secret, and their correctness can be checked independently. This eliminates the need for a trusted third party to generate the parameters. The transparency of the parameters ensures that the system is fair and unbiased. This is a significant advantage over systems that rely on a trusted setup, as it reduces the risk of centralization and control.
Reducing Trust Assumptions
By using transparent parameters, VPS reduces the number of trust assumptions required by the system. The only trust assumption is that the parameters are generated correctly. This is a much weaker assumption than trusting a third party to generate secret parameters. The reduction in trust assumptions makes the system more robust and easier to audit. This is particularly important for systems that are used in high-stakes environments, such as finance or healthcare.
Recursion Strategies
Recursion is the process of verifying a proof of a proof. In proof systems, recursion is used to create succinct proofs that can be verified quickly. Verifiable Proof Systems uses recursion strategies to create proofs that are both succinct and verifiable. The recursion is applied to the admission boundary, not the entire computation. This allows the system to create proofs that are small and fast to verify, while still ensuring that the action is authorized.
Succinct Proofs
The recursion strategy allows VPS to create proofs that are succinct. This means that the proof is small in size, making it easy to store and transmit. The proof is also fast to verify, allowing the system to operate in real-time. The succinctness of the proof is a key advantage for systems that are used in distributed environments, where bandwidth and latency are critical.
Scalability
The recursion strategy also improves the scalability of the system. By creating succinct proofs, VPS can handle a large number of actions without a significant increase in verification time. This makes the system suitable for high-throughput environments, such as cloud computing or IoT. The scalability of the system is a key factor in its adoption, as it allows organizations to deploy the system at scale without compromising performance.
Comparison of Design Methodologies
| Feature | Traditional Proof Systems | Verifiable Proof Systems |
|---|---|---|
| Arithmetization Focus | Entire computation flow | Admission boundary check |
| Constraint Model | Static permissions | Dynamic, scoped to predicted effect |
| Commitment Scheme | Input binding | Identity and effect binding |
| Trusted Setup | Often required | Transparent parameters |
| Recursion | Full proof recursion | Boundary-specific recursion |
Key Takeaways
- VPS separates computation, authority, and consequence at a single admission boundary.
- Arithmetization focuses on the admission check, not the entire computation.
- Constraint models are dynamic and scoped to the predicted effect of the action.
- Commitment schemes bind the proposer's identity to the predicted effect.
- Transparent parameters reduce the need for a trusted setup.
- Recursion strategies create succinct proofs that are fast to verify.
- The system records every decision, including refusals, creating a complete audit trail.
- VPS is a research initiative, and its methods are described in CEAK-PRO 1.0.
Frequently Asked Questions
What is the main difference between VPS and traditional proof systems?
The main difference is that VPS focuses on the admission boundary, where a proposed action is checked against a fixed policy. Traditional systems often focus on proving the correctness of the entire computation.
Does VPS require a trusted setup?
VPS aims to minimize the need for a trusted setup by using transparent parameters. This reduces the risk of compromise and increases the trust in the system.
How does VPS handle recursion?
Is VPS a commercial product?
VPS is a research initiative. It is not a commercial product. The methods described are part of a conceptual framework published in CEAK-PRO 1.0.
What are the five assurance conditions?
The five assurance conditions are independent evidence, bounded authority, verified identity, state continuity, and declared constraints. All five must be met for an action to be admitted.
How does VPS ensure accountability?
VPS ensures accountability by recording every decision, including refusals. This creates a complete audit trail that can be used to investigate any issues.
Can VPS be integrated with existing systems?
Yes, VPS is designed to be modular and can be integrated with existing infrastructure. The admission boundary can be added to existing systems without requiring a complete overhaul.
What is the status of the VPS research?
The VPS research is ongoing. CEAK-PRO 1.0 is a conceptual working paper. Formal models and an implementation are in development for a companion paper.
Conclusion
Verifiable Proof Systems offers a distinct approach to verifiable authority by focusing on the admission boundary. This approach differs from traditional proof systems in its use of arithmetization, constraint models, commitment schemes, trusted setups, and recursion strategies. By separating computation, authority, and consequence, VPS provides a robust framework for ensuring that actions are authorized and accountable. For teams interested in exploring these design methodologies, to discuss a design-partner pilot.