
Verifiable Proof Systems (VPS) helps partners identify potential risks before engaging in a pilot by using boundary definition tools to map where authority, evidence, and consequence intersect. This guide explains how VPS separates computation from authority, how the AgenticX-DYE tool surfaces weak boundaries, and how the CEAK-PRO 1.0 framework structures a four-week pilot to establish a baseline for risk assessment.
Boundary Definition Tools
Boundary definition is the process of explicitly marking where a system's authority ends and where external consequences begin. In autonomous infrastructure, the line between a proposed action and an executed consequence is often blurred. VPS provides custom tools for defining these systems boundaries, written in DARKc, a formally verified fail-closed compiler and syntax. These tools allow partners to visualize the exact points where a system holds permission to act.
The Role of DARKc
DARKc is the underlying syntax used to define the constraints of a system. Because it is a fail-closed compiler, it ensures that if a boundary condition is not explicitly met, the system defaults to a safe, non-executing state. This approach prevents the "silent drift" that often occurs in complex software environments where permissions expand over time without explicit review.
Mapping Authority vs. Computation
VPS distinguishes between computation and authority. Computation is the generation of a candidate action, which carries no permission. Authority is bounded permission over a named object under explicit limits. By using boundary definition tools, partners can map these two concepts separately, ensuring that a fluent model output is never mistaken for a valid permission grant.
The CEAK-PRO Framework
The CEAK-PRO 1.0 framework is a published conceptual working paper that outlines the architecture for verifiable authority. It is available under DOI 10.5281/zenodo.23092344. The framework proposes a single boundary with three planes: Proposal, Admission, and Execution. This structure ensures that every action is checked against a fixed policy before it can affect authoritative state.
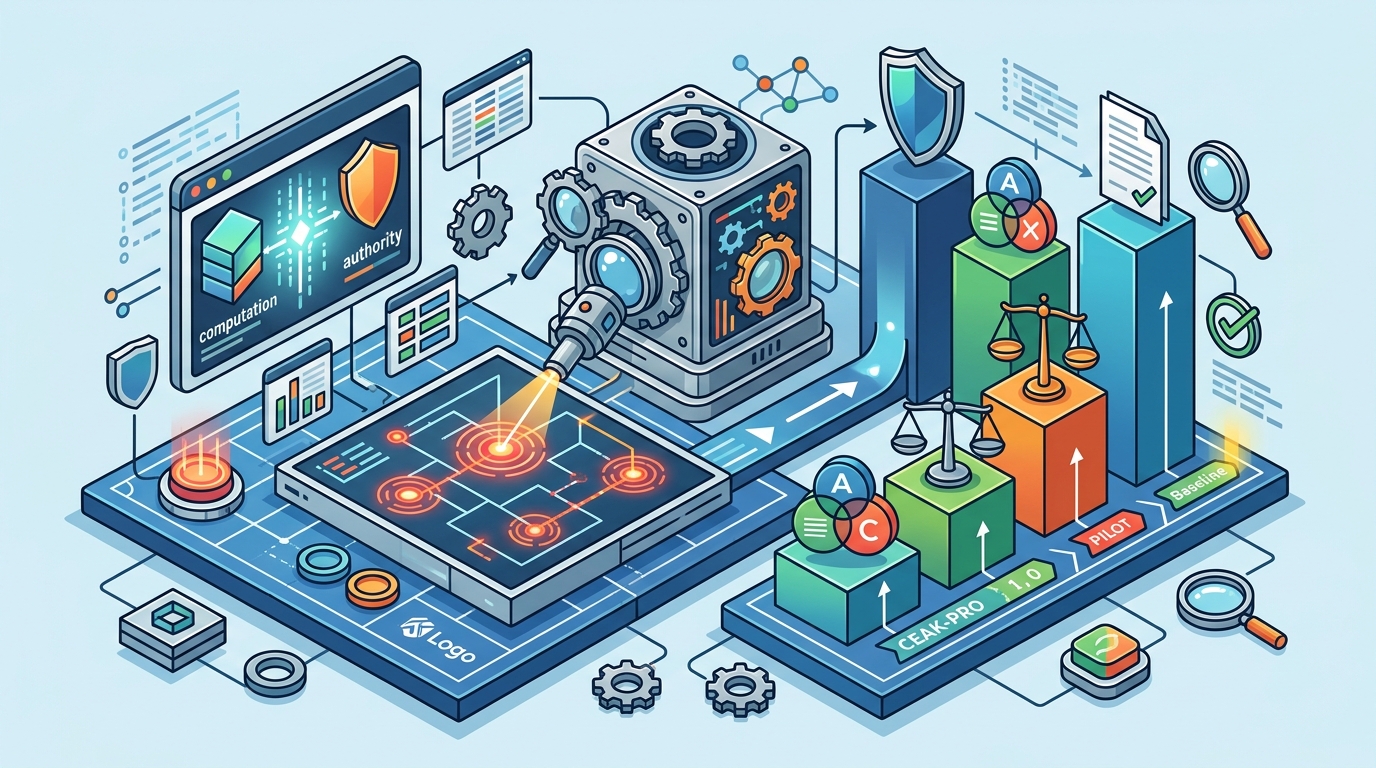
Plane A: Proposal
Plane A is the untrusted zone where models, planners, and humans propose actions. It holds no authority over production state. By isolating proposals here, VPS ensures that the mere generation of an idea does not trigger any physical or digital change.
Plane B: Admission
Plane B is the admission boundary. It performs a small, deterministic check of the attempt and its predicted effect. Admission requires five conditions to hold together: independent evidence, bounded single-use authority, verified workload identity, state continuity, and satisfied declared constraints. If any condition fails, the action is refused and the refusal is recorded.
Plane C: Execution
Plane C is minimal. It carries out only what Plane B authorized and records the outcome. This separation ensures that the execution layer is as small and predictable as possible, reducing the surface area for unexpected behavior.
AgenticX-DYE and Boundary Drift
AgenticX-DYE is a tool that surfaces the points where system boundaries are weak, drifted, or non-existent. In many organizations, boundaries are not static; they shift as new tools are integrated or as permissions are granted for specific tasks and then forgotten. AgenticX-DYE helps partners identify these gaps before they become security incidents.
Identifying Weak Boundaries
The tool analyzes the interaction between the proposing system and the admission boundary. It highlights areas where evidence is missing or where authority has been granted without a corresponding human sponsor. This is critical because a single incident of agentic actions can result in significant financial and legal exposure.
Documenting Gaps
By identifying weak boundaries, VPS helps partners document where the evidence stops. This documentation is not a guarantee of safety, but it provides a clear map of the current risk landscape. It allows teams to prioritize which boundaries need reinforcement before a pilot begins.
Pilot Structure and Baseline Agreement
VPS offers a four-week, fixed-fee pilot for design partners. The goal of this pilot is not to deploy a final product, but to establish a baseline for risk assessment. In week one, partners and VPS agree on specific criteria for success and risk mitigation. If these criteria are met, the pilot closes with a letter of intent.
Week One: Baseline Establishment
The first week is dedicated to defining the baseline. This includes identifying the specific systems to be assessed, the current state of boundary definitions, and the key risks that need to be addressed. This baseline is crucial for measuring the effectiveness of the boundary definition tools.
Weeks Two to Three: Assessment and Tooling
During the middle of the pilot, VPS applies its boundary definition tools and AgenticX-DYE to the partner's systems. This phase involves mapping the current authority structures and identifying where they are weak or non-existent. The results are documented in a claim ledger, which records stated assumptions, explicit non-claims, and their respective falsifiers.
Week Four: Review and Intent
The final week is a review of the findings. Partners and VPS discuss the gaps identified and the potential risks. If the criteria agreed upon in week one are met, the pilot concludes with a letter of intent to move forward with further collaboration.
Risk Mitigation and Evidence
Risk mitigation in the context of verifiable authority is about making changes detectable and recording each decision, including refusals. VPS does not claim to prevent all unauthorized actions, but it provides the infrastructure to ensure that every decision at the boundary is recorded. This creates an audit trail that can be used for internal review or external assessment.
The Claim Ledger
VPS maintains a public claim ledger containing 115 entries. These entries document the assumptions made in the research, the explicit non-claims, and the falsifiers for each claim. This transparency helps partners understand exactly what the framework does and does not do. It prevents the overstatement of capabilities that often leads to false expectations.
ROI and Baseline Measurement
ROI is measured with each partner against a baseline agreed in week one. VPS does not present generic savings figures, as these would be unsupported without specific partner data. Instead, the focus is on the quality of the evidence produced and the clarity of the boundary definitions. This approach ensures that the value of the pilot is tied to the specific needs of the partner's infrastructure.
Key Takeaways
- Boundary definition tools written in DARKc help map where authority ends and consequences begin.
- The CEAK-PRO 1.0 framework separates computation, authority, and consequence at one admission boundary.
- AgenticX-DYE surfaces points where boundaries are weak, drifted, or non-existent.
- A four-week pilot establishes a baseline for risk assessment and closes with a letter of intent if criteria are met.
- The claim ledger documents assumptions, non-claims, and falsifiers to ensure transparency.
- Admission requires five conditions: independent evidence, bounded authority, verified identity, state continuity, and satisfied constraints.
- VPS is a research initiative, not a certifier, and does not claim compliance with specific standards.
- ROI is measured against a partner-specific baseline, not generic industry figures.
Frequently Asked Questions
What is the primary purpose of the VPS pilot?
The primary purpose of the VPS pilot is to help partners identify potential risks before engaging in a larger deployment. It establishes a baseline for risk assessment and documents where boundaries are weak or non-existent.
How does VPS define a system boundary?
VPS defines a system boundary as the point where a proposed action either becomes a consequence or is refused. This boundary is checked against a fixed policy that requires five assurance conditions to hold together.
What is DARKc?
DARKc is a formally verified fail-closed compiler and syntax used by VPS to write custom tools for defining system boundaries. It ensures that if a boundary condition is not met, the system defaults to a safe state.
Does VPS guarantee that a system is secure?
No, VPS does not guarantee that a system is secure or that it prevents all unauthorized actions. Instead, it finds and documents gaps, records each decision, and makes changes detectable.
What is the CEAK-PRO 1.0 paper?
CEAK-PRO 1.0 is a published conceptual working paper that outlines the architecture for verifiable authority. It is available under DOI 10.5281/zenodo.23092344 and describes the three-plane boundary model.
How long does the pilot last?
The pilot lasts four weeks. It is a fixed-fee assessment that closes with a letter of intent if the criteria agreed in week one are met.
Is VPS affiliated with any standards body?
No, VPS is not affiliated with any standards body. It is a research initiative focused on developing infrastructure for verifiable authority.
Conclusion
Identifying risks before a pilot requires a clear understanding of where authority ends and consequences begin. Verifiable Proof Systems provides the tools and framework to make these boundaries explicit. By using boundary definition tools, the CEAK-PRO framework, and AgenticX-DYE, partners can map their current risk landscape and establish a baseline for future collaboration. To discuss a design-partner pilot, .